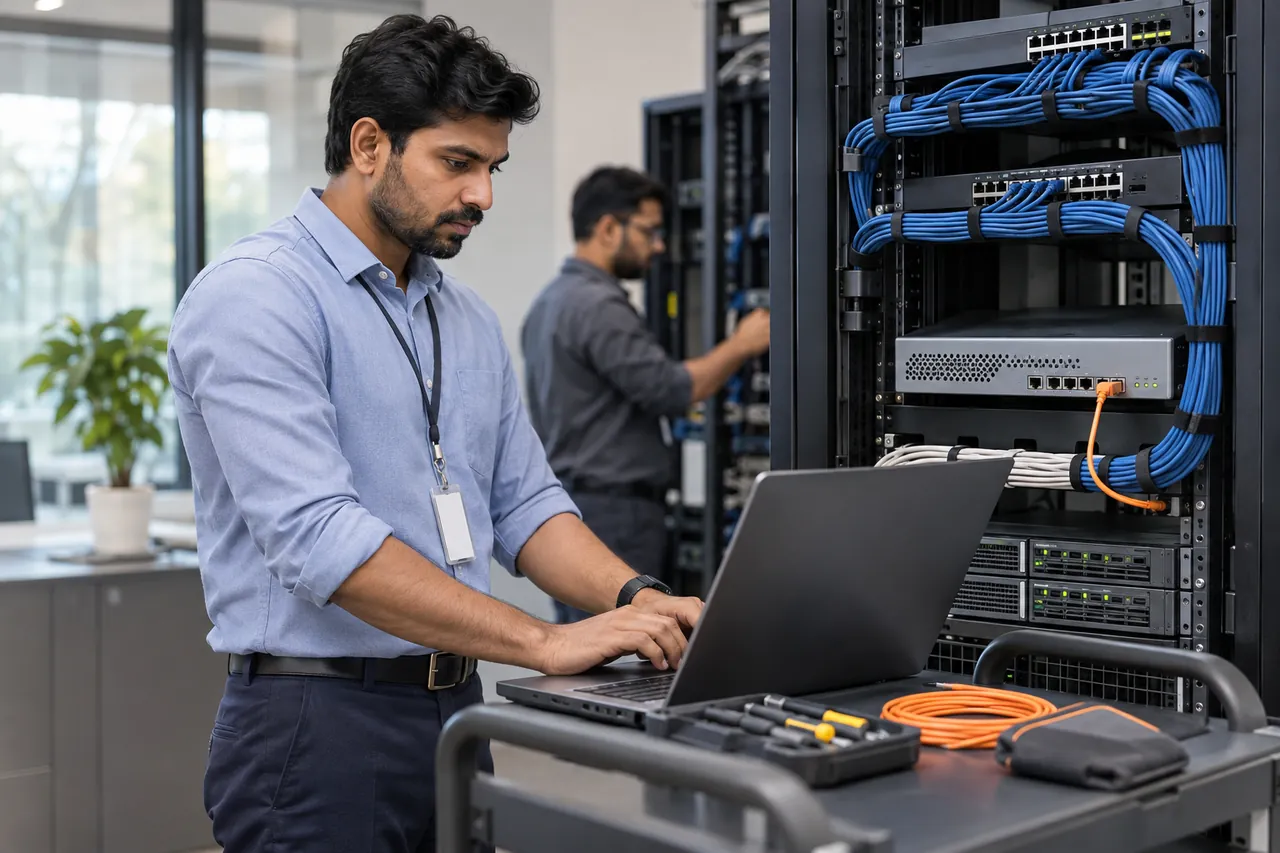

Protect laptops and workstations through consistent configuration, controlled privileges and checks that continue after deployment.
Start with the device's purpose
An endpoint is part of a business workflow, not simply a machine with antivirus installed. A finance laptop, shared reception workstation and administrator device may need different access and applications. Begin by identifying the owner, the information handled and the tasks the device must support. This helps determine the controls needed without creating restrictions that make ordinary work impossible.
Keep an inventory that shows the operating system, support status, assigned user and management coverage. Include remote devices that rarely connect to the office network. A baseline cannot be enforced reliably on devices that are missing from the management system. Agree how personal devices may access business information and which activities require an organisation-managed endpoint.
Use a tested configuration as the starting point
Vendor and recognised industry baselines provide a more dependable starting point than a collection of settings copied from unrelated articles. Microsoft's security-baseline guidance describes recommended configurations and their security implications. Select the baseline that matches the product and version, then test it against the applications and working practices in your environment.
Typical areas to review include local administrator rights, screen locking, disk encryption, firewall settings, browser controls and unnecessary services. Document any exceptions and the reason for them. Keep recovery keys protected and accessible to authorised support staff. Enabling encryption without a reliable recovery process can create an avoidable operational problem when a device or account changes.
Make maintenance part of the baseline
A secure configuration gradually loses value if software remains unsupported or updates do not reach remote devices. Schedule maintenance, track failed installations and confirm that required restarts occur. Cover browsers, document tools, firmware and other important applications as well as the operating system. Remove unused applications to reduce the number of components that need to be maintained.
The NCSC's device guidance covers the device lifecycle, including provisioning, management and retirement. Use that lifecycle view when assigning responsibilities. Someone should own enrolment, monitoring, lost-device handling and secure erasure. The same standard should follow a laptop when it moves between employees, rather than depending on the care taken by its original owner.
Connect protection to a response process
Endpoint protection and detection tools are most useful when alerts reach someone who can assess them. Agree which alerts need immediate investigation, how an affected device can be isolated and who approves actions that may interrupt work. Confirm that the tool is functioning, receiving updates and reporting from every in-scope device. An installed agent that has stopped communicating is a coverage gap.
Run safe, approved checks to confirm the baseline is applied. Sample devices from different teams and locations, and compare their effective settings with the intended policy. Ask users to perform representative tasks during the pilot. Resolve application incompatibilities through controlled changes instead of granting permanent administrator rights as a quick workaround.
Keep exceptions visible
Maintain an exception list with an owner, expiry date and review criteria. Reassess devices that cannot meet the baseline because of old software or hardware. Track management coverage, unsupported devices, update failures and unresolved high-priority alerts. These measures show whether the baseline is operating across the fleet, rather than merely existing in a configuration document.